For finance and insurance software · GoBD
An audit trail your auditor can verify.
Bookings, payments, policies: kernable records every change as a signed event. Nothing is overwritten, every balance has its history, and kernable verify proves it.
The history is the system, not an afterthought.
In most systems the current balance is the truth and the history is a log on the side. In kernable the history comes first, and the balance follows from it:
- 01
Audit tables someone forgot to fill in→Every change recorded, automaticallyEvery booking, correction and approval is an event, with who made it and for whom.
- 02
Corrections that overwrite the original→Corrections are new entriesThe original stays as it was; a correction is recorded next to it, as accountants expect.
- 03
"Trust us" when the auditor asks→Proof instead of promisesSigned and hash-chained;
kernable verifyshows any change, removal or reordering. - 04
Two requests, one account, a race→One change per account at a timeCommands on the same account run strictly one after the other, so rules always see the real balance.
- 05
Customer data stuck in the history→Erasable when the law says soPersonal fields go to an encrypted vault and can be erased, while the bookings stay.
An account in one file.
Your rules decide; kernable stores, signs and orders. The same in TypeScript, Python or Rust.
import { Kernable, Rejected, domain } from "@kernable/sdk";

const account = domain("ledger").aggregate("account", { balance: 0, frozen: false });

account.apply("Deposited", (state, data: { amount: number }) => { state.balance += data.amount; });
account.apply("Withdrawn", (state, data: { amount: number }) => { state.balance -= data.amount; });
account.apply("Frozen", (state) => { state.frozen = true; });

account.command("Withdraw", (state, data: { amount: number }) => {
  if (state.frozen) throw new Rejected("Account is frozen");
  // One command per account at a time: the balance here is always the real one.
  if (data.amount > state.balance) throw new Rejected("Insufficient funds");
  return [{ type: "Withdrawn", data }];
});

await new Kernable({ key: "ledger.key" }).worker(account).run();
Every event carries the signed request that caused it: who, for whom, and why.
Built for the questions auditors ask.
kernable doesn't certify you, but it covers the technical controls behind these requirements, in your software and from the first day.
- Traceability and immutability
Every change recorded in order; nothing stored is ever changed.
GoBD - Protected audit logs
Tamper-evident history, checked by
PCI DSS Req. 10 · ISO 27001kernable verify. - ICT protection and backup
Signed messages, mutual TLS, key rotation, documented backup and restore.
DORA Art. 9 · Art. 12 - Erasure of personal data
Customer data in a vault, erased by a signed event; the bookings stay.
GDPR Art. 17
Where kernable stops: failover is automatic with a standby and a witness, but every write goes through one primary, and availability still needs your runbook and backups. Each control in detail: Compliance in the docs →
Build your ledger with us.
From an architecture review of your current system to the first domain in production: we help your team model accounts, bookings and corrections as events, in the language you already use.
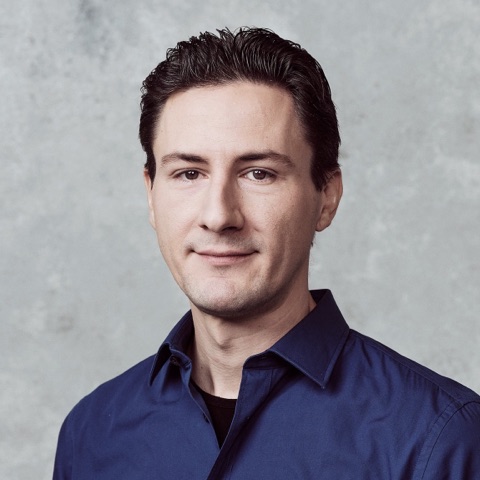
Twenty years of shipping software, the last seven designing the architecture other engineers build on. Author of comby, the event sourcing and CQRS framework that carries multiple commercial platforms in regulated markets. kernable brings the same model to teams that work in any language.
LinkedIn →[ Early access ]
Build on kernable before 1.0.
kernable is in private preview. Tell us what you're building, and we'll send you the binaries and the docs.